ShinyHunters Shopped Pornhub Watch Histories, Then Claimed It Seized an FBI Jobs Site

ShinyHunters spent December 2025 shopping a map of what Pornhub Premium customers searched, watched, and downloaded. In the last week of September 2026 the same brand told reporters it had seized an FBI jobs site, planted a banner that read as if the page belonged to the crew, and walked off with terabytes of personnel and applicant files. The FBI has not confirmed the theft. It has confirmed it is investigating unauthorized activity on FBIJobs.gov. The distance between those two sentences is the point. A crew that blackmails people for adult watch histories is now claiming it can embarrass the agency that is supposed to hunt it, and it says the new job is not about Bitcoin.
The Pornhub file never stopped being the more intimate crime. Pornhub did not lose passwords in that incident. It did not lose card numbers. It did not lose government IDs. What the crew says it took is the behavioral layer: emails, rough locations, video URLs and titles, keywords, whether a clip was watched or downloaded, and timestamps, tied to Premium accounts. The group put the haul at about 94 gigabytes and 201,211,943 analytics records and wanted Bitcoin not to publish them. Row count is not headcount. One subscriber can generate thousands of events. A single email plus a month of titles is still enough to write an extortion note that sounds informed.
Who actually held the smut log
Pornhub, through parent company Aylo, posted a notice on December 12, 2025. It said an unauthorized party had reached analytics data stored with Mixpanel, that the hit involved a limited set of events for some Premium users, and that this was not a breach of Pornhub’s own login or billing stack. The company said affected accounts were secured, that it had hired investigators, and that it had notified authorities and the vendor. Reuters was able to partially authenticate a sample. ShinyHunters showed reporters rows it said belonged to 14 Premium users. District 4 Labs matched details for six of them to older breach dumps. Partial authentication is not a full chain of custody. It is enough to treat the sample as real.
Mixpanel’s answer was a denial with a date attached. The company told reporters it found no sign the adult-site records left during its November 2025 smishing incident or any other breach of its systems. It said the data was last accessed by a legitimate employee account at Pornhub’s parent company in 2023. If that cutoff is accurate, the archive is historical, the contract-era dashboard may already have been stale, and the fight is over who was supposed to delete a sex-life log when the analytics relationship ended. Historical can still ruin a person. A 2023 row with a workplace email and a video title does not become harmless because the vendor’s last incident was in November 2025.
The November incident was real for other customers. Mixpanel spotted an SMS phishing campaign on November 8, 2025. OpenAI said some API users were touched. SoundCloud said roughly 28 million accounts, about a fifth of its base, had data exposed. The pattern fits the crew’s usual door: smish or vish an employee, then walk into a SaaS console that already holds everyone else’s logs. ShinyHunters told Reuters the Pornhub file came out of that incident. Mixpanel said a thorough review with outside experts did not support that claim. Security researchers have floated the boring alternatives. A separate phish of someone who still had old exports. An insider who walked a dump out and sold it under a famous name. The crew has an incentive to staple every haul to a known incident. The vendor has an incentive to isolate every haul from its last incident. Users sit between those incentives.
A brand that kept the logo and changed the ask
ShinyHunters has been a theft-and-extortion name since about 2019. It does not encrypt hospitals for a living. It steals tables and sells silence. French police arrested alleged affiliates in June 2025. A French national, Sébastien Raoult, was extradited to the United States years earlier. The brand kept working. Google has tracked overlapping crews, including UNC6240, through voice-phishing waves against Salesforce customers in 2025. Staff were tricked into connecting a malicious app. Qantas, Allianz Life, luxury houses, Adidas, and a Google Salesforce instance showed up in the blast radius. In May 2026 the same name was attached, in public reporting, to claims against Canvas and Vimeo as well as the still-unresolved Pornhub extortion.
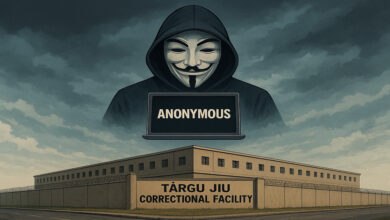
The FBI claim is a different pitch. On or about September 21, 2026, the group told 404 Media, The New York Times, TechCrunch, Axios, and The Register that it had used a previously unknown bug in Oracle PeopleSoft, the human-resources software behind the bureau’s recruiting stack, and then moved into Amazon Web Services GovCloud. It claimed two to three terabytes covering current and former employees and job applicants: names, agent status, emails, phone numbers, home addresses, and in some tellings spouse and sibling data, employment history, and medical information. It named HR systems, a service it called MedLink, and Criminal Justice Information Services. It defaced FBIJobs.gov with a fake seizure notice. The site later sat on a maintenance or unavailable message. Oracle and Amazon did not immediately confirm a new pre-authentication bug. The FBI told reporters the point of breach was still undetermined, whether a third party or the bureau’s own enterprise, and that personnel had been warned to protect themselves while the probe continued.
404 Media and others checked a sample on the order of 5,000 records and found some names and phone numbers that matched public or previously breached data. Matching a name is not proof the row came out of an FBI database this week. CBS News noted that distinction on September 23. The crew’s demand was also new. It told reporters the job was not financially motivated. It wanted the FBI, including Director Kash Patel and a cyber official, to retract or correct a public warning the group says contains false allegations about how it operates. It gave a deadline measured in days. A Bitcoin address is a business model. A demand that a law-enforcement bulletin be rewritten is a grievance. Both can be lies. Neither one gives a Pornhub subscriber their search history back.
Why a watch log is still the sharper harm
A leaked shopping cart is embarrassing. A leaked week of adult search terms can end a marriage, a clearance, a pulpit, or a campaign. The people most exposed were not anonymous casual visitors. They were Premium subscribers, the cohort that paid and therefore left a stronger identifier. Location fields in analytics packages are often coarse. Coarse is enough next to a workplace email. Aylo has spent years telling advertisers and banks that the platform cleaned up after the 2020 card revolt and the later identity-verification reset. A leak of Premium viewing history undercuts that pitch even if the core vault never opened. Intimate telemetry is the product a marketer buys. It is also the product a blackmailer buys.
Europe already treats sex-life data as a special category under GDPR. A file of titles and timestamps is a test of whether that category means anything when the processor is in another country, the contract ended years ago, and the attacker is a Telegram handle. The AEGIS Alliance has watched the same vendor-to-victim hop in other files, including the 700Credit auto-finance breach and the RFID card flaw that sat in office badges long before anyone treated it as a product defect. Third parties hold the interesting data because first parties do not want to build the tooling. When the third party wobbles, the first party sends a blog post.
Major outlets have not confirmed that the full Pornhub dump was published as a public free-for-all. That is not comfort. Extortion crews do not need a front-page leak to do damage. They sell slices to smaller shops. They quote one video title in a phishing mail and wait for the click. Messages that cite a specific clip are not proof the sender has 94 gigabytes. They are proof the sender read a sample. Do not click a link that claims to verify a Premium account. Do not pay a stranger. Change the email on any account that used the same address. Watch identity channels even though cards were supposedly untouched, because stuffing crews will try the address everywhere else.
The lesson is not that sites should stop measuring. They will keep measuring. The lesson is that a dashboard built to optimize thumbnails is also a dossier, and a dossier that outlives the contract is nobody’s dashboard anymore. Pornhub can lock its own vault. It cannot unsay a 2023 row that surfaced under a ransom note in 2025. The FBI can take a jobs portal offline and warn its own people. It cannot, by doing that, make the earlier adult file less specific. The crew’s logo moved from a sex-site shakedown to a claimed breach of the bureau. The harm that already had names on it did not move with the logo.
The AEGIS Alliance will keep the hacker and technology desks on the leak-site claims, the vendor denials, and any regulator who treats adult telemetry as ordinary marketing data. Ordinary marketing data does not usually arrive with a watch history attached, and it does not usually end with a fake seizure banner on a federal jobs page.