Britain’s PSTI Act Made admin and 12345 a Legal Problem for Smart Doorbells, Routers, and Fridges
On April 29, 2024, a password that used to be a suggestion became a legal duty in the United Kingdom. The Product Security and Telecommunications Infrastructure regime, built on the 2022 Act and the 2023 security regulations, told manufacturers they could no longer ship covered consumer connectable products with a universal or easily guessable default password. “admin” is the famous one. So is “12345.” So is the string printed in a PDF that every unit in a product line shares. A device may still arrive with a credential if that credential is unique to the unit and is not generated in a way that makes the next serial number obvious, or if the setup forces the buyer to choose one before the gadget will join a network. The headline that Britain “banned passwords” is wrong. Britain banned the password everyone already knows.
Two quieter duties sit beside the password rule, and they may matter more once the factory sticker is gone. Manufacturers have to publish a way for owners and researchers to report security holes. They have to publish, in public, the minimum period during which the product will receive security updates. A statement of compliance has to travel with the product. Those three lines track the ETSI EN 303 645 baseline that has become the global floor for consumer Internet-of-Things gear. The point is not to make a kettle into a bank vault. The point is to stop a kettle from being drafted into someone else’s botnet because the password was printed on the bottom and never changed.
The Office for Product Safety and Standards enforces the regime. The government has described that enforcement as risk-based, pragmatic, and proportionate, which is regulator language for “we will not fine every tiny seller on day one, and we will not ignore a company that keeps shipping junk.” The National Cyber Security Centre has said non-compliance can be a criminal offence. The ceiling cited in official guidance is a fine of up to £10 million or 4 percent of qualifying worldwide revenue, whichever is higher. That is a maximum, not an automatic bill. Importers, distributors, and the retailers who put their own name on a hub are inside the net. If a broadband provider markets a router under its own brand, the law can treat that provider as the manufacturer. The factory in another country is not the only defendant.
The covered pile is the stuff of a British living room and a British nursery: speakers, televisions, doorbells, baby monitors, cameras, phones, tablets, games consoles, fitness trackers, bulbs, plugs, kettles, thermostats, ovens, fridges, and washing machines, so long as they are consumer connectable products made available in the UK. Products already governed by other safety regimes, including many medical devices and smart meters, sit outside this particular password law because they were never unregulated. The loophole that mattered was the cheap connected toy that was not a medical device and not a meter and still shipped with “admin.”
Mirai Was the Exhibit, Not the Exception
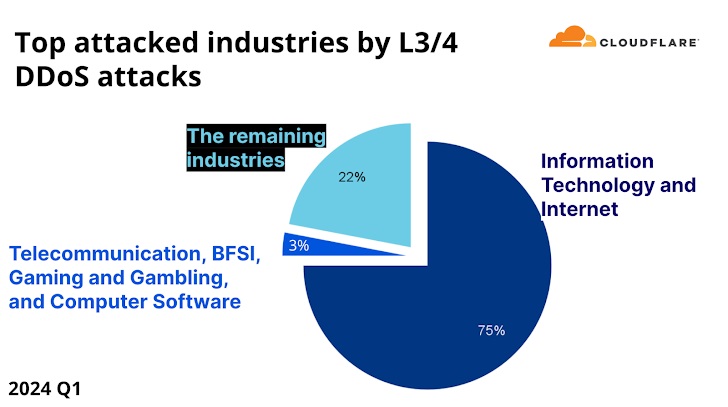
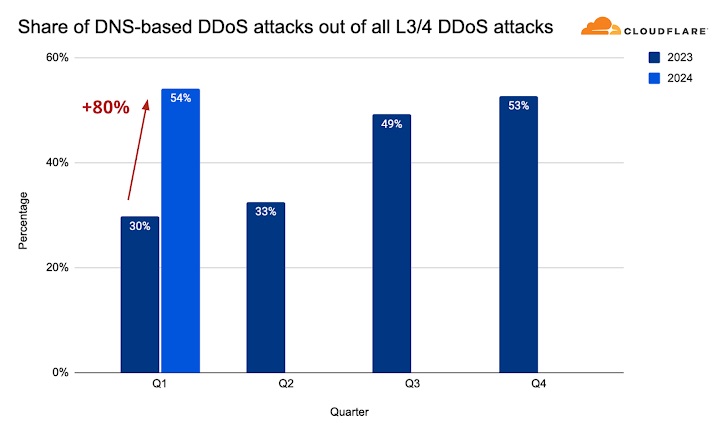
The government’s own press release, the day the duties took effect, named the exhibit. In 2016 the Mirai botnet compromised on the order of 300,000 smart products that still used weak default credentials, then aimed them at major internet services and knocked out access for a large part of the U.S. East Coast. That was not a sophisticated spy novel. It was a scan of the public internet for devices that still answered to the password in the manual. Variants of that code have kept showing up in distributed-denial-of-service traffic for years, because the economics did not change. A camera that costs less than a takeaway dinner will not grow a security team unless the law makes the absence of one expensive.
Early enforcement numbers need to be read as a sample, not as a census. The OPSS Delivery Report for 2024 to 2025, published on GOV.UK on July 30, 2025, describes a targeted look at connected-home, consumer-lifestyle, and child-related products. In that assessment, OPSS looked at 82 products and found varying levels of non-compliance in 75 percent of the products that were in scope of the exercise. That is a serious finding about the shelves investigators chose to pull from. It is not proof that three quarters of every smart device in Britain is unlawful. A risk-based regulator goes where it expects trouble. The honest sentence is narrower and still damning: when inspectors went looking in the categories most likely to sit in a child’s room or a hallway, most of what they examined was missing at least part of the new floor.
The update-window duty is where the law stops being a slogan and starts showing up on support pages. A buyer can now compare two smart plugs not only on price but on how long the maker promises security fixes. Consumer broadband analysts noted that BT, in September 2025, extended the published minimum security support for the Smart Hub 2 from eight years to ten, running into May 2028. TalkTalk’s own product-security page, updated in July 2025, listed end dates in public, including March 2026 for the FAST 5364 and FAST 5464 hubs. Whether a particular hub is still the right buy is a separate question. The new fact is that the end date is no longer a rumor told by a forum. It is a disclosure the seller can be asked to stand behind.
Britain was not inventing the idea from nothing. California’s Senate Bill 327, passed in 2018 and effective January 1, 2020, already told makers of connected devices to stop shipping unique-to-nothing passwords. Manufacturers hate maintaining a special insecure version for one market, so a hard rule in a large market tends to raise the floor in smaller ones. The UK version went further on paper by tying the password ban to a published vulnerability contact and a published support period, and by arming a national product regulator with turnover-linked fines. The voluntary U.S. Cyber Trust Mark asks companies to opt in. PSTI does not ask.
Europe moved on a parallel track and then pulled ahead on reporting. The EU Cyber Resilience Act entered into force on December 10, 2024. Most of its product obligations do not fully apply until December 11, 2027. The reporting piece arrived sooner. From September 11, 2026, manufacturers of in-scope products with digital elements have had to report actively exploited vulnerabilities and severe security incidents to ENISA and the relevant national CSIRT, through a single reporting platform, on a clock that starts with a 24-hour early warning. Those reports cover products already on the market, not only devices designed after the Act. A UK password ban and an EU 24-hour exploit report are different tools. Together they describe the same shift: security claims are no longer marketing copy. They are filings.
None of this makes a compliant doorbell safe in every other way. A product can have a unique password, a vulnerability email address, and a three-year update promise, and still ship with a sloppy mobile app, a cloud account that shares too much, or a firmware process that lags a public exploit by months. The same week PSTI took effect, research on widely used Chinese pinyin keyboard apps showed what happens when the encryption around the act of typing is junk. The AEGIS Alliance covered that exposure of keystrokes from nearly a billion users. A law about the password on a smart plug does not encrypt a keyboard. It does remove the oldest, dumbest welcome mat.
Households are left with a practical reading, not a victory lap. If a device was in the house before April 29, 2024, the law does not crawl backward through the skirting boards and change its password. Owners of older cameras and bulbs still have to retire “admin” themselves, or retire the device. If a device was supplied after that date and still boots into a shared default, that is a compliance question for OPSS, not a personal failing. The useful habit is to read the support-period line the way people read an energy label: a cheap plug with a short window is not cheap once it becomes an unpatched hole on the home network. Routers count. The hub with the provider’s logo on it is not a gift that lives outside the statute.
The NCSC has also said it is highly likely the same ideas will be pressed, over time, onto business equipment and not only the junk in the living room. Offices are full of the same cameras and badges and printers, bought on a different purchase order and ignored for the same reason. A criminal who wants a foothold does not care whether the camera watches a nursery or a loading dock. For the official text of the consumer duties, start with the National Cyber Security Centre’s explanation and the government announcement from the day the rules bit. More from this desk is in Tech News, International News, and Hacker News, including the later account of how Google took apart a shadow network that had been using phones as quiet infrastructure.