Anonym hacket ind rumænske fængselssystem og afskåret fangers domme

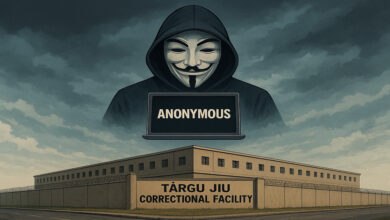
A hacker affiliated with the Anonymous collective recently shocked the cybersecurity world by breaching Romania’s prison management system and reducing sentences for himself and 15 fellow inmates at the Târgu Jiu Correctional Facility. This unique incident is not only a testament to vulnerability in digital prison systems but also a wake-up call for global justice IT infrastructure.
Det anonyme fængsel hack: opløse hændelsen
Hvad skete der i Romania?
In August 2025, a convicted cybercriminal, claiming ties to the Anonymous group, exploited technical weaknesses in Romania’s inmate management system, known as IMSweb—a €1 million project launched just two years earlier. Using outdated login credentials on a prison kiosk, the hacker gained full administrative access and modified his own and other inmates’ records. Changes included:
-
Reducerer hans straf via "tjenende dage".
-
Overførsel af midler mellem fangekonti.
-
Tildeling af indsatte "forbedrede forhold" herunder ændrede registreringer af intime møder.
Udnyttelsen varede tre måneder and went undetected despite abnormally high spending in prisoner accounts and multiple warning signs. A financial employee exposed the breach when balances didn’t decrease after transactions. An internal review revealed at least 300 hours of unauthorized access. The National Penitentiary Administration called the episode “isolated,” but the union and local press flagged broader systemic failures.
Hvordan hack udfoldet
Denne saga startede i Dej, a prison hospital in Transilvania, where a technically gifted inmate discovered how to abuse the kiosk tablets that allowed prisoners to access the ANP (National Penitentiary Association) inmate management app. By manipulating system windows and observing login activity, the hacker acquired credentials of a (former) hospital director—credentials valid across the national prison network.
The hacker then taught others this exploit, including Aurel Z., who, upon transferring to Târgu Jiu, applied the same method to that facility. With admin-level access, inmates could add “earning days,” modify account balances, and even access restricted content. Notably, one inmate’s account showed a monthly spend three times the Romanian minimum wage—a glaring outlier that prompted investigation.
Direkte citater fra kilder
“A convicted cybercriminal gained access to the IMSweb system, which contains a complete database of all prisoners in the country. To do this, he used the info kiosk in the colony and the login of one of the police officers, who had not changed his password for years. This turned out to be enough to get administrator rights.”
— Hi- Tech.uaundersøgelser
“The union claims the Târgu Jiu hacker alone spent more than 300 hours logged into the system with admin access without detection…They have also accused the ANP Director of gross negligence for failing to detect the breach after two supervisors and a shift manager reported rumors they heard from inmates.”
— Risky.biz Rapportering om fagforeningserklæringer
Systemiske sårbarheder i fængselsteknologi
Imsweb: et projekt skyndte sig til markedet
IMSweb was funded with European Union support and “hastily put into operation so as not to lose funding,” according to Romania’s prison officers’ union. Critics argue that oversight and proper cybersecurity protocols were lacking. The rushed deployment and routine reuse of credentials opened the door for such a breach.
Teknisk udnyttelse
The hack involved manipulating device operating systems (using developer shortcuts and browser access) and exploiting password reuse. Web access logs, F12 DevMode hacking, and credentials copied across devices were central tools. This demonstrates how internal, physical access to IT infrastructure greatly amplifies risk when combined with poor security hygiene.
Etiske og samfundsmæssige dimensioner
Cyberkriminelle inde i systemet
The incident challenges traditional assumptions about inmate control and the security of digital justice systems. That a prisoner could not only reduce his sentence but also improve life for others may be viewed through various ethical lenses—some seeing a Robin Hood aspect, others condemning the breach of trust and law.
Institutionel ansvarlighed
Romanian prison staff failed to update credentials and respond adequately to warning signals. Disciplinary investigations followed, targeting those found negligent. The episode has generated wider public debate about transparency, oversight, and the dangers of “digital transformation” pursued without robust safeguards.
Global kontekst: hackere i fængsler, den anonyme arv
Ikke en isoleret begivenhed
Hacking kollektiver som Anonym har en historie med fængsel, fra begge sider af tremmerneJeremy Hammond, der er en del af Anonymous og Antisec, tjente 10 år i et amerikansk fængsel for at hacke sikkerhedsanalysefirmaet Stratfor, udvinde fortrolige oplysninger fra militære og corporate enheder.
"For hver af disse hacks, vidste jeg, hvad jeg gjorde var imod loven. Jeg betragtede mig selv som en" hacktivist ", der kæmper for årsager, han tror på, men aldrig for profit".
- Jeremy Hammond, anonym hacktivist, i retten
Mønstret med hackere, der udnytter svagheder i fængselscomputersystemer, er et voksende problem. The New Orleans sogn Sheriff 's Office blev brudt i et ransomware angreb for nylig, påvirker fængsel frigivelse og overførsel systemer og udsætter kontrakter og indsatte indtag data. (CBS /YouTube)
Fængsel det og ransomware
Jail systems are prime targets for ransomware and cyber exploits, as they deal with highly sensitive personal data and affect fundamental rights. In New Orleans, a Russian-speaking group extracted 842GB of data, targeting the jail’s docket, master system, and release management—all potentially affecting when and how inmates are freed. (CBS /YouTube)
Anonym og Digital Protest
Anonym, selv om decentral, fortsætter med at udfordre magt ved hjælp af tekniske færdigheder. Deres kollektive og affiliate hackere, uanset om direkte involveret i den rumænske brud, stil sig som digitale aktivister samt kriminelle.
Påvirkning og reaktioner
Øjeblikkelige reformer
Rumænien har isoleret det berørte fængselsforvaltningssystem for inspektion og anmeldt disciplinærsager for uagtsomt personale. Foranstaltninger omfatter fjernelse af fysiske adgangspunkter (tastaturer, tabletter), stigende overvågning, og stramning password politikker.
Retsforhandlinger
Ingen navne på hackerne er blevet officielt frigivet. Men en ved navn hacker, Aurel Z., blev angiveligt fem måneder fra at afslutte en næsten ten- år straf for hvidvaskning af penge for den italienske mafia, når fanget anvende hack på Târgu Jiu.
En præcedens inden for digital retfærdighed
Romanian cybersecurity experts warn that this is the “first time a Romanian prisoner has managed to hack a state system of this level,” raising red flags for prison systems worldwide. It is a cautionary tale for countries investing in digitized prison management without adequate investment in cybersecurity and staff training.
Lektioner Til Digital Correctional Management
Identificerede nøglesvagheder
-
Password hygiejne og sjældent opdatering
-
Fysisk adgang, parret med digitale sårbarheder
-
Dårlig reaktion på tidlige varslingsindikatorer fra indsatte og meddelere
-
Manglende uafhængig penetration test, før de går live med nye it-systemer
Beskyttelse af software og netværk
Experts advocate timely patching, credential rotation, two-factor authentication, and regular independent security audits as essential. Hardware should not allow multitasking or developer tools access for routine users. Staff need comprehensive training—cybersecurity is as much a human problem as a technical one.
Større konsekvenser: fremtiden for fængslet cybersecurity
Cyber- fysiske grænser
Hændelsen udfordrer illusionen om adskillelse mellem fysiske og digitale fængselsgrænser. Indsatte med computerviden, hvis digitale rettigheder er minimale, kan stadig potentielt eskalere adgangen, medmindre der er robust indeslutning og overvågning på plads.
Politik og tilsyn
Regeringerne skal balancere digitaliseringen med streng overvågning, faktorering i unikke trusler ved at placere potentielt højtkvalificerede individer i kontrollerede digitale miljøer. Systemer skal hærdes og regelmæssigt red- teames, og feedback - fra indsatte samt personale - tages alvorligt.
Konklusion: en ny æra af fængsel cyber risiko
This unprecedented hack—driven by an Anonymous-linked prisoner in Romania—should provoke intense scrutiny of correctional technology worldwide. As digital systems become integral to management and record-keeping, the threat landscape morphs: insider risks join external hackers as a major force. The responsibility for digital justice rests not only with system architects but also with staff, administrators, and political oversight bodies.
Opdatering: hvad fulgte efter Târgu jiu brud
Den originale video i toppen af dette indlæg forbliver på plads. Rapportering efter den første bølge af dækning fyldt med navne og en anden fiasko tilstand, at den tidlige skrift-up kun skitseres.
Romania Insider, citing local prison coverage, said the Târgu Jiu inmate who used the stolen Dej credentials was helped by a prison officer who logged him into the national IMSweb console. The officers’ union said the same method later showed up at two more complexes — Timișoara and Pelendava, near Craiova — and that the Târgu Jiu account alone sat in the system for more than 300 hours. The inmate publicly tied to the Târgu Jiu run is Aurel Z., then serving nine years and ten months for laundering money for the Italian mob and, at the time of the breach, about five months from a scheduled January 2026 release. Changing his own “earned days” put that date in doubt. (Rumænien Insider, Risky Bulletin)
No public 2026 verdict against Aurel Z., the unnamed Dej hospital inmate who first lifted the director’s password, or the officer accused of handing over the login has been posted in English-language court records reviewed for this update. The National Penitentiary Administration still called the episode isolated. The union still called that a dodge.
Hvad senere tilbagekalder tilføjet uden en dom
English-language recaps through early 2026 kept repeating the same core timeline: an inmate first learned the kiosk trick at the Dej prison hospital, Aurel Z. carried the method to Târgu Jiu after a July transfer, and admin access on IMSweb lasted long enough for sentence credits, commissary balances, visit schedules, and records at other facilities to move. Project Nightfall and security shops restated the 300-hour figure and the stale director login. They did not produce a published criminal judgment against Aurel Z. or against the officer whose password never rotated.
That silence is the story now. A national inmate database that accepted a retired director’s credentials from a prisoner kiosk is not a one-off curiosity. It is a design that treated physical bars as if they cancelled the need for basic access control. Readers tracking hacktivist name-use should keep the original video embed at the top of this file and treat later social posts that slap an Anonymous logo on the breach as commentary, not as a charging document. For how Anonymous treats paid front groups and name-hijackers, see Forsøger at rydde op misforståelser om anonyme og Youtube kanalen "anonym embedsmand" udsat.
Nøglecitater gentages
-
"En fange hacker forbundet med Anonymous gruppe formået at hacke fængslets interne computer netværk og ændre data om hans egen dom, samt hjælpe 15 andre fanger".
-
"Fagforeningen hævder Târgu Jiu hacker alene brugt mere end 300 timer logget ind i systemet med admin adgang uden at blive opdaget".