شخص مجهول اخترق نظام السجن الروماني وقطع عقوبة السجناء

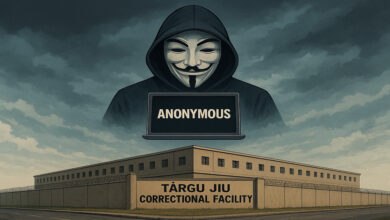
A hacker affiliated with the Anonymous collective recently shocked the cybersecurity world by breaching Romania’s prison management system and reducing sentences for himself and 15 fellow inmates at the Târgu Jiu Correctional Facility. This unique incident is not only a testament to vulnerability in digital prison systems but also a wake-up call for global justice IT infrastructure.
اختراق سجن مجهول: كشف الحادث
ماذا حدث في (رومانيا)؟
In August 2025, a convicted cybercriminal, claiming ties to the Anonymous group, exploited technical weaknesses in Romania’s inmate management system, known as IMSweb—a €1 million project launched just two years earlier. Using outdated login credentials on a prison kiosk, the hacker gained full administrative access and modified his own and other inmates’ records. Changes included:
-
تخفيض عقوبته عن طريق "أيام تعلم"
-
تحويل الأموال بين حسابات السجناء
-
منح النزلاء "الظروف المرتجلة" بما في ذلك السجلات المعدلة من اللقاءات الحميمة
استمر الاستغلال ثلاثة أشهر and went undetected despite abnormally high spending in prisoner accounts and multiple warning signs. A financial employee exposed the breach when balances didn’t decrease after transactions. An internal review revealed at least 300 hours of unauthorized access. The National Penitentiary Administration called the episode “isolated,” but the union and local press flagged broader systemic failures.
كيف كشف الإختراق
هذه الـ(ساغا) بدأت في (ديج), a prison hospital in Transilvania, where a technically gifted inmate discovered how to abuse the kiosk tablets that allowed prisoners to access the ANP (National Penitentiary Association) inmate management app. By manipulating system windows and observing login activity, the hacker acquired credentials of a (former) hospital director—credentials valid across the national prison network.
The hacker then taught others this exploit, including Aurel Z., who, upon transferring to Târgu Jiu, applied the same method to that facility. With admin-level access, inmates could add “earning days,” modify account balances, and even access restricted content. Notably, one inmate’s account showed a monthly spend three times the Romanian minimum wage—a glaring outlier that prompted investigation.
اقتباسات مباشرة من المصادر
“A convicted cybercriminal gained access to the IMSweb system, which contains a complete database of all prisoners in the country. To do this, he used the info kiosk in the colony and the login of one of the police officers, who had not changed his password for years. This turned out to be enough to get administrator rights.”
— مرحبا تيكواالتحقيق
“The union claims the Târgu Jiu hacker alone spent more than 300 hours logged into the system with admin access without detection…They have also accused the ANP Director of gross negligence for failing to detect the breach after two supervisors and a shift manager reported rumors they heard from inmates.”
— المخاطرة. الإبلاغ عن البيانات النقابية
مواطن الضعف النظامية في تكنولوجيا السجون
مشروع عجل إلى السوق
IMSweb was funded with European Union support and “hastily put into operation so as not to lose funding,” according to Romania’s prison officers’ union. Critics argue that oversight and proper cybersecurity protocols were lacking. The rushed deployment and routine reuse of credentials opened the door for such a breach.
المتفجرات التقنية
The hack involved manipulating device operating systems (using developer shortcuts and browser access) and exploiting password reuse. Web access logs, F12 DevMode hacking, and credentials copied across devices were central tools. This demonstrates how internal, physical access to IT infrastructure greatly amplifies risk when combined with poor security hygiene.
الأبعاد الأخلاقية والمجتمعية
الجرائم السيبرانية داخل النظام
The incident challenges traditional assumptions about inmate control and the security of digital justice systems. That a prisoner could not only reduce his sentence but also improve life for others may be viewed through various ethical lenses—some seeing a Robin Hood aspect, others condemning the breach of trust and law.
المساءلة المؤسسية
Romanian prison staff failed to update credentials and respond adequately to warning signals. Disciplinary investigations followed, targeting those found negligent. The episode has generated wider public debate about transparency, oversight, and the dangers of “digital transformation” pursued without robust safeguards.
السياق العالمي: القراصنة في السجون، وإرث مجهول
لا حدث معزول
"الجماعات المهووسة" تاريخ مخزن مع السجن من جانبي القضبان(جيرمي هاموند) الذي هو جزء من (أنونيموس) و(أنتيسيك) قضى 10 سنوات في سجن أمريكي لإختراق شركة التحليل الأمني (ستراتفور)
"لكل من هؤلاء القراصنة، كنت أعرف ما كنت أفعله كان ضد القانون. كنت أعتبر نفسي "محارباً محارباً لأسباب يؤمن بها" "لكن ليس من أجل الربح"
- جيريمي هاموند، مخترق مجهول الهوية، في المحكمة
ونمط القراصنة الذين يستغلون نقاط الضعف داخل نظم حواسيب السجن هو شاغل ناشئ. تم اختراق مكتب عمدة (نيو أورليانز) في هجوم على الفدية في الآونة الأخيرة، مما أثر على نظم الإفراج عن السجناء ونقلهم ومصادرة العقود وبيانات المقبوض عليهم.CBS/اليوتيوب
سجنه و فدية
Jail systems are prime targets for ransomware and cyber exploits, as they deal with highly sensitive personal data and affect fundamental rights. In New Orleans, a Russian-speaking group extracted 842GB of data, targeting the jail’s docket, master system, and release management—all potentially affecting when and how inmates are freed. (CBS/اليوتيوب
احتجاجات مجهولة ورقمية
ولا تزال مجهولة الهوية، وإن كانت لا مركزية، تتحدى السلطة باستخدام المهارات التقنية. وهؤلاء المخترقون الجماعيون والمنتسبون، سواء كانوا متورطين بشكل مباشر في الخرق الروماني أم لا، يعتبرون أنفسهم ناشطين رقميين ومجرمين.
الأثر والرؤى
الإصلاحات الفورية
وقد عزلت رومانيا نظام إدارة السجناء المتضررين للتفتيش وأعلنت إجراءات تأديبية للموظفين المهملين. وتشمل التدابير إزالة نقاط الدخول المادية (اللوحات الرئيسية، اللوحات)، وزيادة المراقبة، وتشديد سياسات كلمة السر.
الإجراءات القانونية
لم يتم بعد إطلاق أي أسماء من القراصنة رسمياً على أي حال، واحد اسمه هاكر, Aurel Z., وتفيد التقارير أنه بعد خمسة أشهر من الانتهاء من الحكم الذي يناهز عشر سنوات على غسل الأموال للمافيا الإيطالية عند القبض على المخترق Târgu Jiu.
سابقة في العدالة الرقمية
Romanian cybersecurity experts warn that this is the “first time a Romanian prisoner has managed to hack a state system of this level,” raising red flags for prison systems worldwide. It is a cautionary tale for countries investing in digitized prison management without adequate investment in cybersecurity and staff training.
Lessons for Digital Correctional Management
مواطن الضعف الرئيسية
-
النظافة الصحية لكلمات المرور والتحديث غير المتواتر
-
الوصول المادي، مقترنة بمواطن الضعف الرقمية
-
سوء الاستجابة لمؤشرات الإنذار المبكر من السجناء والمخبرين
-
عدم وجود اختبار مستقل للاختراق قبل العيش مع نظم جديدة لتكنولوجيا المعلومات
ضمانات البرامجيات والشبكات
Experts advocate timely patching, credential rotation, two-factor authentication, and regular independent security audits as essential. Hardware should not allow multitasking or developer tools access for routine users. Staff need comprehensive training—cybersecurity is as much a human problem as a technical one.
الآثار الأكبر: مستقبل أمن الفضاء الإلكتروني في السجون
Cyber-Physical Borders
The incident challenges the illusion of separation between physical and digital prison boundaries. ولا يزال بإمكان النزلاء الذين لديهم معارف حاسوبية، نظراً لمحدودية الامتيازات الرقمية، أن يصعّدوا إمكانية الوصول إلا إذا كان هناك احتواء ورصد قويين.
السياسات والرقابة
ويجب على الحكومات أن توازن الرقمنة بالرقابة الصارمة، مع مراعاة التهديدات الفريدة التي يشكلها وضع الأفراد ذوي المهارات العالية في البيئات الرقمية الخاضعة للمراقبة. ولا بد من تصعيد النظم وإعادة صياغتها بصورة منتظمة، وتلقي ردود الفعل من النزلاء ومن الموظفين على محمل الجد.
الاستنتاج: عهد جديد من مخاطر الفضاء الإلكتروني
This unprecedented hack—driven by an Anonymous-linked prisoner in Romania—should provoke intense scrutiny of correctional technology worldwide. As digital systems become integral to management and record-keeping, the threat landscape morphs: insider risks join external hackers as a major force. The responsibility for digital justice rests not only with system architects but also with staff, administrators, and political oversight bodies.
Update: What Followed the Târgu Jiu Breach
الفيديو الأصلي المتضمن في قمة هذه الوظيفة يبقى في مكانه التبليغ بعد الموجة الأولى من التغطية المليئة بالأسماء وطريقة الفشل الثانية التي رسمت في وقت مبكر فقط.
Romania Insider, citing local prison coverage, said the Târgu Jiu inmate who used the stolen Dej credentials was helped by a prison officer who logged him into the national IMSweb console. The officers’ union said the same method later showed up at two more complexes — Timișoara and Pelendava, near Craiova — and that the Târgu Jiu account alone sat in the system for more than 300 hours. The inmate publicly tied to the Târgu Jiu run is Aurel Z., then serving nine years and ten months for laundering money for the Italian mob and, at the time of the breach, about five months from a scheduled January 2026 release. Changing his own “earned days” put that date in doubt. (رومانيا, نشرة المخاطر)
No public 2026 verdict against Aurel Z., the unnamed Dej hospital inmate who first lifted the director’s password, or the officer accused of handing over the login has been posted in English-language court records reviewed for this update. The National Penitentiary Administration still called the episode isolated. The union still called that a dodge.
ما أضيف لاحقاً بدون حكم
English-language recaps through early 2026 kept repeating the same core timeline: an inmate first learned the kiosk trick at the Dej prison hospital, Aurel Z. carried the method to Târgu Jiu after a July transfer, and admin access on IMSweb lasted long enough for sentence credits, commissary balances, visit schedules, and records at other facilities to move. Project Nightfall and security shops restated the 300-hour figure and the stale director login. They did not produce a published criminal judgment against Aurel Z. or against the officer whose password never rotated.
That silence is the story now. A national inmate database that accepted a retired director’s credentials from a prisoner kiosk is not a one-off curiosity. It is a design that treated physical bars as if they cancelled the need for basic access control. Readers tracking hacktivist name-use should keep the original video embed at the top of this file and treat later social posts that slap an Anonymous logo on the breach as commentary, not as a charging document. For how Anonymous treats paid front groups and name-hijackers, see محاولاً توضيح أفكار خاطئة عن مجهول و قناة (يوتوبي) كشفت.
Recap
-
مخترق سجين مرتبط بجماعة مجهولة تمكن من اختراق شبكة الحاسوب الداخلية للسجن وتغيير البيانات عن حكمه الخاص، وكذلك مساعدة 15 سجيناً آخرين
-
"النقابة تدّعي أن مخترق (تارغو جيو) قضى أكثر من 300 ساعة على دخول النظام دون أن يكتشف"