Flamingchina hævder en 10-petabyte tyveri fra Kinas Tianjin Supercomputer og lister træk for cryptocurrency

The first public receipt was not a ministry statement. It was a Telegram post. On February 6, 2026, an account calling itself FlamingChina dropped sample files and a price list. The claim attached to those files was simple enough to sound fake. The operator said it had lived inside the National Supercomputing Center in Tianjin for about six months, pulled more than 10 petabytes of material, and would sell a preview for thousands of dollars or the whole stack for hundreds of thousands, payable in cryptocurrency. A BreachForums successor listing under the handle airborneshark1 carried the same pitch around February 4. Forum names change. The sample set is the only object that can be tested.
Ten petabytes is not a stolen inbox. A high-end laptop holds about a terabyte. Ten petabytes is 10,000 of those drives. If even a slice of the advertised haul is real defense work, the damage is not the crypto invoice. The damage is a map of who computes what on a shared national machine, and who left a VPN domain unlocked long enough for a botnet to walk the aisles. CNN kunne ikke kontrollere datasets oprindelse. Specialister, der kiggede på de første prøver fortalte netværket, at de så ægte. Det hul - eksperter siger, at filerne matcher en liste over Tianjin-lejere, en stat, der ikke siger noget - er stadig hele den offentlige rekord.
Et hotel til andre folks hemmeligheder
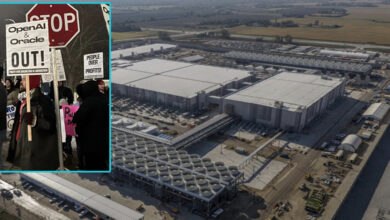
NSCC-Tianjin is not a vault with one customer. It sells cycles. Research institutes, companies, and government shops rent time on the same campus that made global headlines when Tianhe-1 topped the TOP500 list in late 2010. Official descriptions put the modern client count near 6,000. That mixed tenant list is why a single intrusion can spit aircraft skins, fusion models, and biology papers out of the same folder tree. Dakota Cary, a SentinelOne consultant who focuses on China, told CNN the sample swath was “exactly what I would expect to see from the supercomputing center.” Most of those customers, he said, would have little reason to keep their own supercomputers.
April reporting named organizations that appeared in the sample set, including the Aviation Industry Corporation of China, the Commercial Aircraft Corporation of China, and the National University of Defense Technology. Some documents carried Chinese markings consistent with secret classification. Other files were technical renderings and animated simulations of bombs and missiles. TechRadar og sikkerhedsanliggender gentog rumfart og våben beskrivelser. Ingen af disse forretninger kunne sætte en regeringsbekræftelse under overskriften. Prøverne er historien indtil nogen udgiver hash, som et andet laboratorium kan matche.
Cary’s second point was the one that should scare operators more than the brand name. He did not describe an elegant zero-day ballet. He described a hole. In his read, and in the account Marc Hofer of the NetAskari blog said he heard from the persona, operators used a compromised VPN domain, then parked a botnet that pulled data to different servers over months. “You can think of it as having a bunch of different servers that you have access to and you’re pulling data through this hole in the security of the NSCC,” Cary said. The method, if true, is not genius. It is patience plus a shared login surface that nobody watched.
Markedet for et lager
Hofer told CNN that only a state or a well-funded lab would have the capacity to work through a 10-petabyte pile and come back with something useful. CNN could not independently verify the account the hacker gave Hofer. That sentence belongs in every rewrite of this file. A sales channel is not a chain of custody. Criminal buyers cannot park 10 petabytes on a consumer NAS and decode missile geometry by the weekend. Intelligence services do not need a dark-web shopping cart if they already collect on Tianjin tenants. The realistic market is smaller than the headline: governments, contractors, and a handful of brokers who already have cold storage and analysts who read Chinese technical documents.
That smaller market still matters. A verified sliver of AVIC or COMAC design data would be a gift to a rival aerospace program. A verified sliver of National University of Defense Technology work would be a gift to anyone mapping Chinese weapons research. The geopolitical cost is not the Telegram invoice. It is the possibility that a shared scientific utility became a reading room. Cary noted that some leaks from China’s cyber ecosystem sell quickly, and that plenty of governments interested in NSCC data may already have pieces of it.
Den oprindelige GhostStory etiket på denne URL var en tidlig branding for den samme påståede indtrængen. Persona sælger nu data er FlamingChina. AEGIS Alliance treats marketing names as stickers. Sample hashes, if anyone publishes them, are the product. Until Beijing issues an incident report or a third party posts a reproducible set, this remains an alleged supercomputer theft with expensive previews. That is already enough to rattle anyone who parked a classified job on a shared national cluster and assumed the landlord’s VPN was someone else’s problem.
Hvorfor delte computer bliver ved med at tabe
A national supercomputing center is a hotel with a science budget. Tenants come and go. Accounts linger. VPN certificates get reused. Research groups share scratch disks because the alternative is waiting in a queue. Defense contractors sit two racks over from a university fusion team because the machine does not care who paid for the cycle. That architecture is efficient. It is also one compromised domain controller away from a catalog of other people’s secrets.
Cary told CNN that poor cybersecurity has been a long-running condition across a wide number of Chinese industries and organizations. China’s own 2025 National Security White Paper listed “robust security barriers for the network, data, and AI sectors” as a priority. Listing a priority is not the same as closing a VPN hole. CNN reached the Ministry of Science and Technology and the Cyberspace Administration of China for comment. Neither office answered in the April 8 report. Silence is not a denial and it is not a confirmation. It is a vacuum that a Telegram sales pitch filled first.
Scale is the other problem. Extracting 10 petabytes without a traffic spike that a monitoring team notices implies either a very quiet pipe or a very inattentive watch floor. Six months is a long time to move a warehouse. Either the exfiltration was throttled to look like ordinary scientific outbound traffic, or the people who should have seen the graph were not looking. Both explanations are ugly for a facility that markets itself as a backbone for aerospace and defense computation. Jeff Wichman, an incident-response director at Semperis, called the alleged theft “shocking and unimaginable” if the military-secret piece holds. Unimaginable is a press word. Unmonitored is the operational one.
Hvad der endnu ikke er sket
No Chinese ministry has published an incident timeline. No independent lab has posted a public hash set that other researchers can match. No court, company, or regulator has confirmed that AVIC, COMAC, or NUDT lost files through Tianjin. Those absences do not make the claim false. They make it unfinished. A 10-petabyte story that stops at Telegram is a story that can still collapse or explode depending on the next file that leaks.
Relaterede filer i dette arkiv sidder i Hacker-nyheder stack, herunder Handala trusler mod Netanyahu flyvning, USA 's likviditetsbrud tilskrevet kinesiske operatørerog Sanktionspakke, der følger. Læsere, der ønsker den bredere infrastruktur beat kan blive på internationale nyheder Det er et skrivebord. Mønsteret på denne side er ældre end FlamingChina. Fælles beregning er delt risiko. Et VPN domæne er en hoveddør. En botnet, der kører i seks måneder er en fiasko at se, ikke et magisk trick.
The AEGIS Alliance will treat the next sample the same way as the first. Name the persona. Name the center. Name the experts who looked. Refuse to launder a sales pitch into a confirmed breach. The warehouse may be real. The receipt is not in yet. National laboratories that sell cycles to 6,000 clients cannot pretend they are closed shops. The tenants who parked classified work on that floor already know what the bill looks like if the samples hold.