اصطدمت البريد بـ 000 29 صندوق مع وصلة موقّعة و نفس المجموعة لا تزال مفيدة بعد يوم الضريبة


موعد التقديم الـ 15 من أبريل متأخر عنا البرمجيات الخبيثة التي ركبت في البريد المزيف IRS ليست كذلك.
On March 19, 2026, Microsoft Threat Intelligence and Microsoft Defender Security Research published the campaign anatomy that security teams had already been seeing in their queues: tax-season mail dressed as refund notices, payroll forms, and EFIN alerts, split between credential-harvesting sites and payloads that install legitimate remote monitoring and management software. The flagship blast on February 10 reached more than 29,000 users at over 10,000 organizations. About 95 percent of the targets were in the United States. Two waves ran between 10:35 and 19:51 UTC. Financial services, technology, and retail absorbed the largest shares, but the intended inboxes clustered around accountants and tax preparers. The write-up lives on the Microsoft Security Blog.
The AEGIS Alliance أقل إهتماماً بالخدعة التقويمية من اختيار الحمولة لم يحتاج المهاجمون إلى زرع تقليدي لقد استخدموا مكاتب مساعدة البرامجيات التي تثق بها بالفعل وهذا هو السبب في أن نفس المجموعات لا تزال مهمة في أيلول/سبتمبر، بعد فترة طويلة من أن يترك آخر استمارة التمديد مكتبا.
مُشاهد مُصوّر مُتطوّر كان مُتصلاً بزيّ
Messages claimed irregular returns had been filed under the recipient’s Electronic Filing Identification Number and pointed to a “Download IRS Transcript View 5.1” button. Amazon SES sent the mail. The button led to smartvault[.]im, a look-alike of the real SmartVault document platform, sitting behind Cloudflare checks meant to keep scanners out. After a fake verification animation, victims received TranscriptViewer5.1.exe — a repackaged ScreenConnect build signed by ConnectWise. Once launched, operators had remote control, credential access, and a beachhead for whatever came next.
That is the design. A signed binary from a vendor that IT departments already allow through the door. Endpoint products that hunt for unknown junk will shrug. A user who thinks the IRS just handed them a viewer will click. The rest of the compromise is quiet. No ransom note. No splash screen. Just a remote session that looks, to a tired firewall, like a technician doing a job.
أخبار هاكر وكشف موجز نفس البحث عن الهدف: فلم يكن الانفجار رذاذ في الأسر المعيشية العشوائية. وكان الهدف من ذلك هو الأشخاص الذين يكون عملهم هو فتح ملحقات ضريبية. هذه مشكلة مختلفة عن الجدة التي تضغط على شفرة (كيو ر)، رغم أن كلاهما ظهرا في نفس الموسم.
عندما أصبح الشاشة أصعب، الطقم تحولت العلامة التجارية
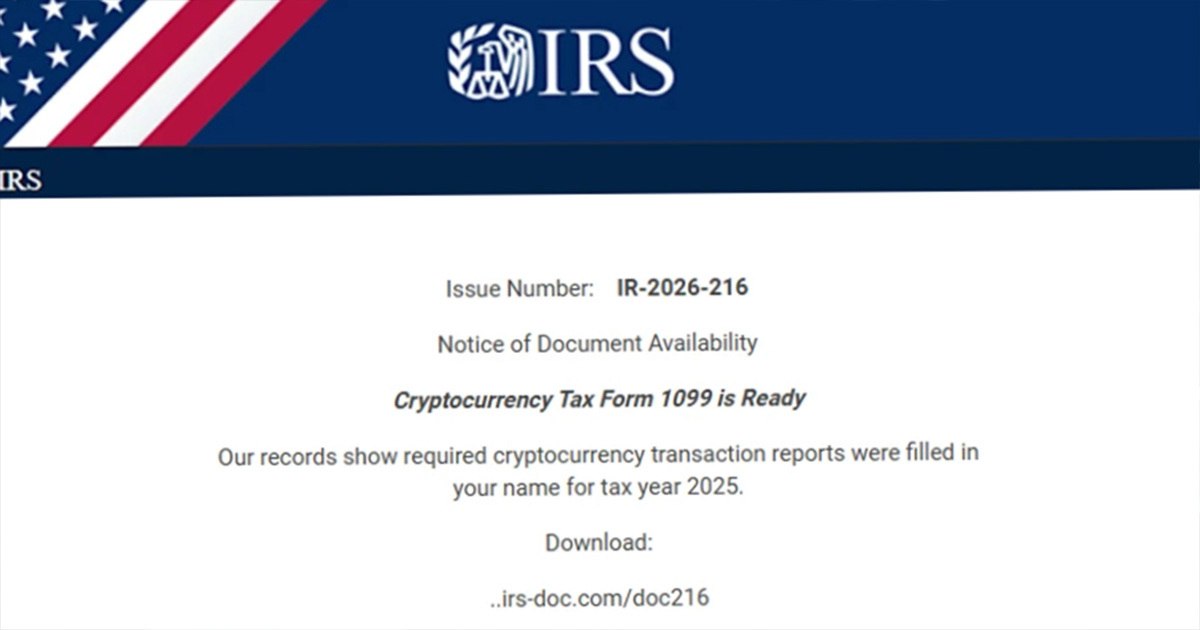
Follow-on waves on February 23 and 27 used subject line “IR-2026-216,” Eventbrite-styled IRS branding, and a “Cryptocurrency Tax Form 1099” lure aimed at higher education. Domains such as irs-doc[.]com and gov-irs216[.]net dropped IRS-doc.msi files that installed ScreenConnect or SimpleHelp. Accounting-firm variants installed Datto. Microsoft’s researchers noted the same trend Huntress quantified industry-wide: RMM abuse up 277 percent year over year, sometimes daisy-chained so no single vendor’s telemetry tells the whole story. Elastic Security Labs researchers Daniel Stepanic and Salim Bitam put the problem plainly — these tools are already trusted inside corporate networks, so they do not trip the alarms reserved for unknown binaries.
Credential-theft kits ran in parallel. Energy365, estimated to push hundreds of thousands of messages a day, wore CPA branding. SneakyLog, also tracked as Kratos, hid QR codes in personalized W-2 attachments that opened fake Microsoft 365 logins and captured multifactor codes. The IRS Dirty Dozen for 2026 again listed impersonation by email and text at the top of the list and repeated the only reliable rule: the agency does not start contact by unsolicited email, text, or social media to demand data or payment. That reminder is on IRS.govلقد كان على إس آر.غوف لسنوات الصناديق لا تزال مفتوحة
The Dirty Dozen also flagged AI-enabled phone impersonation, social-media “tax hacks,” and spear-phishing aimed at tax professionals. Item eleven on that list is the quiet one. It describes “new client” and “document request” mail that delivers malware to steal client files. The February 10 blast was that item at industrial scale. The agency reported more than 600 social-media impersonators during fiscal 2025. None of those accounts needed a ScreenConnect binary. They needed a logo and a sense of urgency.
لماذا تبقى المتاجر الضريبية الجائزة بعد أبريل
ويحمل المستعدون أرقام الضمان الاجتماعي، وبيانات التحويل المصرفي، وعائدات السنوات السابقة لقوائم العملاء بأكملها. صندوق بريدي واحد يسترد أموالا من الغش وسرقة الهوية من نوع موثق في المجرى 700 Credit الخرق الذي كشف حوالي 6 ملايين مشتري سيارات. The professionals Microsoft described are “accustomed to receiving tax-related emails during this period,” which is exactly why the lures work. CISA, NSA, and MS-ISAC have already warned that portable RMM executables can run as a local user without a full install, a path used against federal civilian networks.
The new problem is calendar-blind. Extension season, amended returns, and the next estimated-payment cycle keep the same inboxes hot. Signed RMM binaries will still look like IT doing its job. Organizations that only locked down during March and April are leaving the same door on the latch. A firm that banned ScreenConnect in February and never checked SimpleHelp or Datto in May has not closed the campaign. It has changed the costume.
Quarterly estimated payments in September and January keep the same anxiety in the same mailboxes. A partner who ignored a fake transcript viewer in February will still open a fake “notice of underpayment” in the fall. Attackers know that. They rent Amazon SES again. They change the subject line. The signed binary stays the same because the trust stays the same.
وظهر نفس النمط في ملفات أخرى للتحالف، بما في ذلك ملفات الإنترنت عدّة استنساخ (ناغيت).. تحذير بنك (فانتوم هاكر)وبعد ذلك الإبلاغ عن كيفية ضرب المشغلين الصينيين لمراكز عمل الخزانة في حادثة الوصول عن بعد-علامات مختلفة نفس الفكرة ثقة الاقتراض، ثم تفرغ الحساب.
ما يقلل في الواقع من فرصة موجة ثانية
Multifactor authentication on mail and financial accounts, conditional access that blocks odd sign-ins, and a written ban on installing any remote-access tool that IT did not request are the minimum. Staff should open IRS accounts by typing the official address, never by clicking a button in a message. Suspicious mail can go to ph******@*rs.gov- يتعين على أدوات تحديد النهايات أن تُعلّم المُنظمة المرئية الأولى، والمُساعدة البسيطة، والداتو، وتركيبات لوغمين، وليس مجرد خردة غير موقّعة.
Accounting shops should treat a surprise “transcript viewer” the way a bank treats a surprise wire. Call the person who is supposed to have sent it on a number you already have. Do not call the number in the email. Do not run the exe to “see if it looks real.” A signed ConnectWise binary that nobody in IT ordered is not a tool. It is a key.
Help desks should also assume daisy-chaining. Huntress has described attackers stacking one RMM inside another so that killing ScreenConnect leaves SimpleHelp running. A cleanup that only uninstalls the brand named in a blog post is theater. Pull the unexpected remote-access services, rotate credentials that lived on that box, and treat every token on that machine as burned. The AEGIS Alliance will keep tracking how impersonation campaigns migrate from seasonal lures to whatever deadline comes next, including the broader pattern in أخبار القراصنة و أخبار الولايات المتحدة.
الثقة هي المنتج شعار مصلحة الضرائب هو مجرد ملفوف أي شخص ما زال يعتقد أن الخطر انتهى في 15 أبريل هو قراءة التقويم بدلا من الحمولة.
الجواب