Google Cuts Millions of Hijacked Phones and TV Boxes Out of IPIDEA, a Residential Proxy Pool Used by 550 Threat Groups in One Week

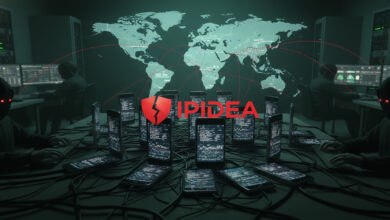
Residential proxies are other people’s phones, routers, and set-top boxes rented out as exit nodes. IPIDEA, Google says, was one of the largest of those pools. In late January 2026 the Threat Intelligence Group and partners took down storefronts, command domains, software-development kits, and marketing sites, then went to court to stop the vendors from selling the kit to people who target unwitting device owners. GTIG’s own count still sits at the center of the story: in a single seven-day window that month, more than 550 tracked threat groups used IPIDEA exit nodes, including crews attributed to China, North Korea, Iran, and Russia.
Google says the hit cut millions of devices out of the pool. Reseller agreements mean a blow to IPIDEA also bruises whoever was renting the same last mile. That is the angle The AEGIS Alliance is keeping. This was not a single botnet takedown with a catchy malware name. It was an attempt to collapse a commodity layer that hundreds of crews share when they need a home IP instead of a data-center range.
How a TV box becomes someone else’s alibi
The pitch to consumers is extra cash for sharing bandwidth. The pitch to buyers is a residential address that will not trip the fraud filters banks and social networks keep for cloud providers. Phishing kits, account-takeover scripts, and credential-stuffing jobs hide behind that ISP address. The homeowner sees a slightly slower evening stream. The investigator sees a Comcast or Verizon range and assumes a person in a living room.
Google’s technical write-up is on the Cloud Threat Intelligence blog. The plainer version is on the GTIG consumer post. Reuters, working off those posts, added the inventory: IPIDEA ran at least 13 residential proxy brands that went offline in the same action. Analysts tied more than 600 Android applications and 3,075 unique Windows files to the network’s command-and-control infrastructure. Play Protect rules were pushed so Android devices would stop talking to those domains. Legal process hit the storefronts so the next landing page would have a name to serve.
Some of those apps were sideloaded. Some rode in through software that promised optimization, a VPN, or a few dollars a month for unused data. The honest version of that market exists. The IPIDEA version, as Google describes it, treated consent as optional and the device as inventory. Once the SDK is on the box, the owner is not a customer. The owner is a route.
Why 550 groups on one network is the number that matters
Threat-intelligence shops usually talk about clusters. A ransomware crew. An APT badge. A fraud shop. The IPIDEA observation flattened those categories. In one week, more than 550 tracked groups used the same exit fabric. That is not a club. That is infrastructure. China-attributed, DPRK-attributed, Iran-attributed, and Russia-attributed crews do not need to like each other to buy the same last mile. They need a price list and an API.
When a network that large is the shared hallway, a takedown has a different shape than a malware sinkhole. You do not “defeat” 550 groups. You make the hallway more expensive. Google said the available pool dropped by millions of devices and that reseller deals would carry the damage into affiliated shops. In July 2026 the same team published a follow-on action against the NetNut residential proxy network, also tracked as Popa, and said the IPIDEA aftermath had taught them that individual networks can look resilient even after a public hit. That sentence is the adult version of the January victory lap. Proxy shops rebuild. The court papers exist so the next storefront is not a clean name.
Related vendor-risk files on this desk include the 700Credit API breach that exposed nearly six million car buyers and the NGate Android malware that cloned tap-to-pay cards. Different products. Same lesson. The device in a pocket is now a workplace for strangers.
What a reader can actually do
No one should sideload a “share your connection” app for a few dollars. That sentence is the only user-facing fix that does not depend on Google’s next lawsuit. Check what is installed. Revoke accessibility and VPN permissions that a weather widget does not need. Factory-reset a cheap Android box that came with extra icons. If a relative was paid to run a bandwidth app, assume the box has been an exit node and treat stored passwords as burned.
Enterprises have a different problem. Residential-proxy traffic is how account takeovers look like commuting customers. Fraud teams that still whitelist “home ISP” ranges as safe are buying the story the proxy shop is selling. The AEGIS Alliance technology and hacker news files will keep that distinction in print: a Comcast address is not an identity. It is a path.
Play Protect helps people who stay inside the official store. It does not help a television stick that never saw the store. It does not help a Windows box that ran a cracked optimizer. GTIG’s file-count on the Windows side is the reminder that this was not only a phone story. Desktops were inventory too.
Disruption is not disappearance
IPIDEA’s brands going dark is a real cost for the operators. Domains seized in court are a real cost. Millions of devices dropping out of a pool is a real cost. None of that retires the business model. The model is older than this brand name. Bulletproof hosts used to sell the same thing with a server in a poorly supervised rack. Residential proxies sell it with a stranger’s living room. When one shop is hit, buyers walk down the hall to the next API.
Google’s July NetNut action was the admission of that hallway. The company framed both operations as a program, not a one-off. Programs are how large vendors describe work they intend to bill as virtue and as market defense. Both can be true. A cleaner Android ecosystem is good for people who own phones. It is also good for a company that sells the phones’ operating system. Readers can hold those facts without doing the vendor’s public-relations work.
The useful test is downstream. Did phishing kits that leaned on IPIDEA exits have to rebuild? Did Play Protect actually stop the 600-plus Android packages from talking home? Did the 13 brand sites stay down or reappear under new registrars? Those are measurable. “One of the world’s largest” is a press phrase. Measurement is the story.
Until that measurement is public, the January action stands as a rare case where a consumer device market was treated as a threat-intelligence target instead of as an advertising audience. The AEGIS Alliance will take that as progress and as incomplete. The next app that offers to pay for idle bandwidth will use softer copy and a different logo. The hallway will still be for rent.