Chinese Hackers Borrowed Former White House Science and Tech Expert’s Name to Phish Inboxes Writing America’s AI Export Rules

El buzón que redacta una sentencia de control de exportación es un premio más tranquilo que un montón de pesos modelo, y ese es el buzón que un equipo alineado con China fue después. A partir del 8 de julio de 2026, Proofpoint later reported, un grupo que rastrea como TA419 abrió el phishing credencial tomando prestado Lynne Edwards Parker, describió allí como el ex director adjunto principal de la Oficina de la Casa Blanca Política de ciencia y tecnología. La misma carrera tomó prestado Heidi Crebo-Rediker, un economista cuya carrera corre por el Departamento de Estado y el Comité de Relaciones Exteriores del Senado. Las notas no pidieron código fuente. Pidieron a la gente política que se uniera a una conversación.
Proofpoint llama a TA419 motivado por el espionaje y alineado por China, y dice que el 1 de octubre de 2026 es el primer informe público sobre el grupo. Desde al menos abril de 2025, ha visto a la gente de Fish TA419 en Estados Unidos y Japón think tanks, contratistas de defensa, universidades y bufetes de abogados. Reuters reported the same day que la ola de julio llegó a menos de 10 personas, incluyendo especialistas en regulación de IA, controles de exportación y estrategia nacional. La etiqueta China es la evaluación de Proofpoint desde la infraestructura y el objetivo. Reuters señaló que la Embajada de China no comentó y que Beijing niega el ciberespionaje. No es una decisión judicial.
Why the borrowed biography had to match the ask
The July messages were written to sound like a favor between colleagues. One version invited the recipient onto a fictitious «AI Policy Advisory Committee.» Another asked for help with a Senate Committee on Foreign Relations report on AI export controls and supply chains. Help Net Security retransmitió la cuenta de Mark Kelly que el email de apertura no llevaba ningún enlace malicioso. El cebo era la respuesta. Sólo después de que alguien escribió atrás llegó una dirección web acortada, prometiendo más material y caminando a través de redirige hacia un acceso a la nube falsificada.
El registro de Crebo-Rediker es por qué encaja el segundo nombre. Ella fue la primera economista principal del Departamento de Estado en los años Obama, había sido jefa de finanzas internacionales para el Comité Senatorial de Relaciones Exteriores, y es una beca mayor En el Consejo de Relaciones Exteriores. Una solicitud de ayuda con un documento del Senado sobre controles de exportación es una nota que generaría carrera. El nombre de Parker hizo el trabajo paralelo para un comité consultivo. Es robótica, directora fundadora de la National Artificial Intelligence Initiative Office, y, en la redacción de Proofpoint, ex directora adjunta de la ciencia oficina.
The Trump administration had already advertised the persona. On 22 December 2024, Donald J. Trump named Parker executive director of the President’s Council of Advisors on Science and Technology and counselor to the director of the Office of Science and Technology Policy. Michael Kratsios was to run that office, and David Sacks, whom Trump called an «AI and Crypto Czar,» was to chair the council. The announcement, carried by Politico y described by Science, promised a «Golden Age of American Innovation» and «America’s technological dominance,» stapling a science panel to a cryptocurrency pitch. That branding handed a later impostor a committee title that already sounded official. The people drafting export-control language were still working in ordinary Microsoft 365 mail. The White House sold the names and left the inboxes easy to phish.
Heidi Crebo-Rediker’s State Department and Senate Foreign Relations background matched the AI export-control report lure.
Reuters identified one recipient as Alex Engler, a former White House official who now heads the University of Pennsylvania’s Center on Media, Technology, and Democracy. Engler said the message, which invited him «to join a new AI policy project,» «felt slightly, nebulously off.» He realized it was an impostor after checking with other people. Parker told Reuters he was one of two people she knew of who had received mail purporting to come from her in early July. She also said, «The United States and China are in a competition around AI. Trying to get people in the AI policy space to reveal information about their AI policy plans — if that indeed was what the objective was — it’s not surprising.»
A small list is the point, not a consolation. Criminal kits spray tens of thousands of inboxes and still function as a business. In December 2025, The AEGIS Alliance reported on the arrest tied to RaccoonO365, un servicio construido para robar Microsoft 365 sesiones en volumen. TA419 apuntaba a la misma clase de robo en una habitación que encaja alrededor de una mesa. El objetivo no era un archivo modelo. Era el hilo donde se estaba redactando una regla de exportación.
What the fake OneDrive page took from a Microsoft 365 login
La cuenta de Proofpoint, escrita para los defensores y no como guía de construcción, describe dos etapas. El primer dominio de julio, driftshare[.]co, mostró una pantalla OneDrive falsa detrás de un control de voltaje de Cloudflare. Un segundo dominio, globalfileshareplatform[.]com, acogió la página adversario-en-el-medio, utilizando un kit personalizado navegador-en-el-browser conocido como BitB sin marco y un Evilginx phishlet para Microsoft 365. La página retransmitió el registro real de Microsoft, incluyendo el código de una sola vez, por lo que la contraseña y el segundo factor fueron escritos donde un operador podía ver.
Scripts on the page drew a file listing and a fake browser window, accepted «Keep me signed in» without the user, and submitted a one-time code after it checked out. The login still succeeded at Microsoft. What the operator kept was the password, the multi-factor code, and the session cookies that mark a Microsoft 365 user as already signed in. Microsoft has described that pattern for years. A copied cookie means the second factor is not asked again.
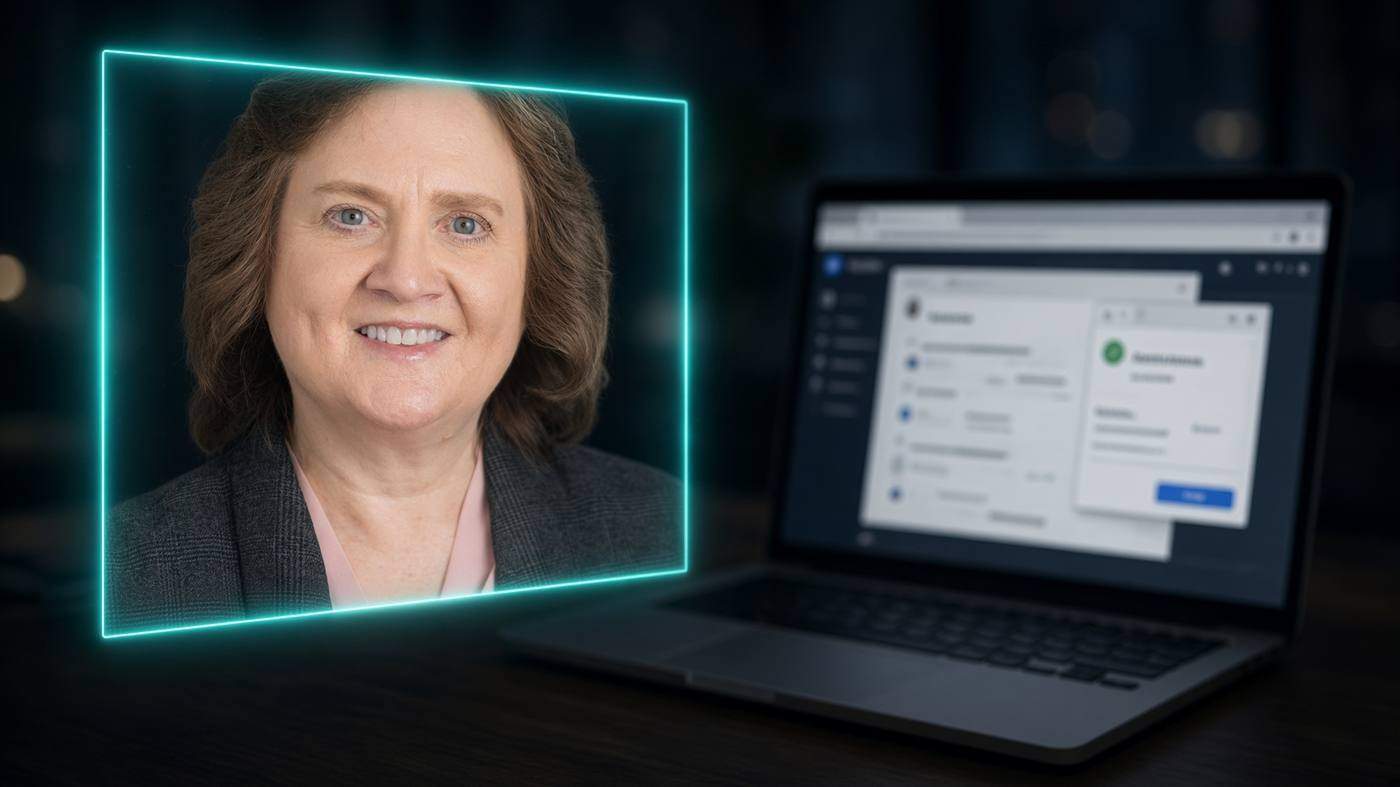
Proofpoint described a counterfeit browser layered over a OneDrive-style share that relayed the real Microsoft sign-in.

Esa charla del 16 de julio de 2026 del desarrollador de Evilginx Kuba Gretzky cubre los kits de relé credencial y los intentos de debilitar el registro resistente al phishing. No es una sesión informativa sobre la TA419. Muestra la misma familia de herramientas Proofpoint dice que este equipo personalizado.
Domains se sentó detrás de Cloudflare y a menudo fueron registrados a través de NameSilo como marcas de archivos compartidos como rápida[. ]online, cirrushare [.]co, y winsync[.]cloud. Others impersonated institutions, including tw-koryu[.]org, the misspellings heritiages[. ]org y heritiage[.]org, y shinjirou[.]info. Unos 2026 mensajes utilizaron un certificado auto-firmado que nombró una ciudad ficticia de Kansas, Millsstad, y una firma llamada Castro Inc. Otros salieron a través de proxies residenciales.
A February lure about military integration of Claude
July was not the first AI impersonation from this group. In February 2026 TA419 posed as a senior Anthropic employee and wrote an AI policy analyst at a United States think tank. The subject line was «Request for Feedback on Military Integration of Claude,» aimed at the fight over military use of Anthropic’s models. The shape matches the summer mail: a believable name, a live dispute, and no login page until someone replies.
Proofpoint has described a separate China-aligned actor, UNK_SweetSpecter, in earlier reporting on the SugarGh0st tool utilizado contra organizaciones que construyen IA generativa. Ese trabajo persiguió a los laboratorios. El correo 2026 de TA419 persiguió a las personas que escriben las reglas bajo las que viven esos laboratorios, y Proofpoint también toma nota de interés alineado por China en las cadenas de suministro semiconductor y de poca profundidad bajo los mismos modelos.
One suspicious feeling will not protect the next inbox
Engler notó algo ligeramente apagado, y luego se comprobó con otras personas. Eso funcionó una vez, para alguien que ya conocía el mundo de Parker. No viaja a un analista junior halagado por un comité que suena oficial. El primer email estaba limpio a propósito, tantos portales no tenían nada que detonar, y el paso malicioso esperó hasta que una conversación de aspecto real había comenzado.
Selena Larson de Proofpoint, hablando el 22 de septiembre de 2026 con el CUBE de SiliconANGLE, discutió cómo las herramientas generativas cambian el aspecto del correo de ingeniería social. Ese segmento no es sobre TA419. Es el problema más amplio alrededor de este incidente. Una nota puede ser gramática, específica, y todavía ser una lure, así que la ortografía rota es una defensa débil para una tienda de políticas.

The 1 October writeup is direct. «TA419 has consistently shown an interest in defense, national security, energy, international relations, and foreign policy targets, predominantly with a nexus to the US and Japan,» it says. «The targeting of AI policy experts represents an extension of that remit rather than a departure from it.» Proofpoint assesses that TA419 «will likely continue targeting think tanks and policy experts working on technologies, and in geographies, of particular interest to the Chinese government,» and that «these campaigns will likely also continue spoofing the identities of real subject-matter experts.»
Passkeys are the control that matches this phish
Un código de una sola vez no detuvo las páginas de julio. El código fue escrito en un relé del propio impulso de Microsoft, y la sesión resultante se mantuvo con el operador. El punto de vista indica a las organizaciones de este objetivo que utilizan el registro de origen resistente al phishing, como los passkeys, que están vinculados al sitio real y no dan un par de contraseñas y códigos para un lookalike. También le dice a los individuos que traten una nota sorpresa de un famoso especialista como pretexto y para comprobarlo en un canal que el remitente no escogió.
Un passkey no rescatará un hilo ya copiado. Lo que cambia es la siguiente respuesta. Los papeles que vale la pena tomar aquí vivieron en el correo ordinario de la nube, no un enclave clasificado, escrito por personas que redactaron el lenguaje de exportación-control AI. Hacker News y International News coverage has followed the high-volume version of the same theft, including a March 2026 Microsoft warning about impostor mail. TA419 is the boutique version: fewer than 10 inboxes, chosen for what those people were about to write. Crebo-Rediker’s biography is on the Consejo de Relaciones Exteriores site, and more of this lane is filed under Noticias at The AEGIS Alliance.









